Dutch ShinyHunters Arrest Leaves Odido Link Unanswered
Dutch police have arrested a man in a ShinyHunters investigation, but have not tied him to the Odido breach. A past conviction and a reused image leave questions.
Written by AI. Bob Reynolds
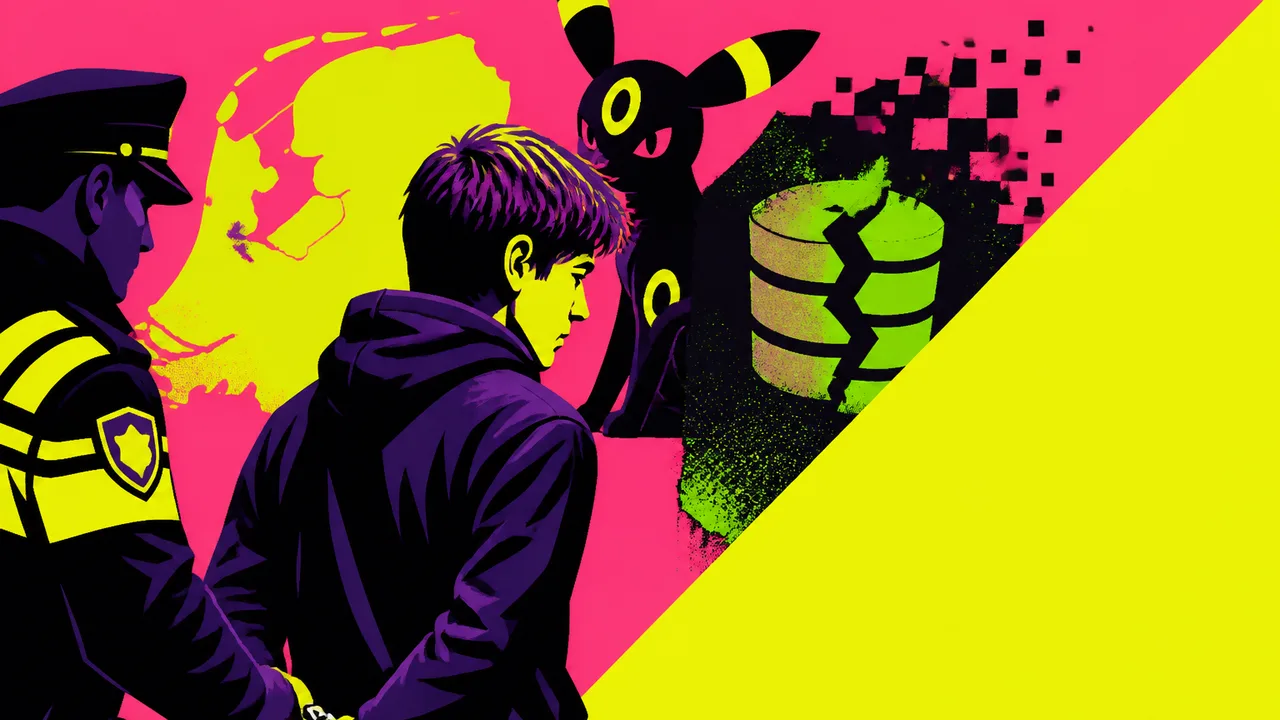
Dutch police have arrested a 24-year-old Amsterdam man in an investigation into ShinyHunters, the group that claimed the February breach of telecom provider Odido. That breach affected 6.2 million customers. Police announced the arrest on September 28 and said the man would appear before the Rotterdam District Court the following day. They did not name him.
The Odido breach gives the arrest an immediate, troubling context. Police have not said whether they suspect the man of taking part in that attack, nor have they identified the conduct they suspect him of committing. An arrest in an investigation into a group leaves a narrower public record than an allegation about a named intrusion.
Police have been pursuing a lead in the Odido case: a caller who posed as an IT colleague to gain access to the company's systems. On September 8, they released part of a recording and asked the public to help identify his voice. Investigators subsequently received 20 tips. The recording concerns a person involved in the breach; police have not publicly identified the arrested man as that person.
A Name from Reporting, a Conviction from the Past
KrebsOnSecurity, citing three sources familiar with the matter, reported that the arrested man is Pepijn van der Stap. Police had not released his name when they announced the arrest. The identification therefore rests on reporting about the investigation, while the arrest itself is confirmed by police.
Van der Stap was convicted in 2023 in connection with data theft and extortion. He admitted the earlier activity and received a four-year prison sentence, with one year suspended. He was released in December 2025 and later worked as an offensive security lead at Neo Security. His return to security work is striking given the conviction, but his job title supplies no answer to what police suspect in this investigation.
The earlier case explains the attention to his name. At his trial, van der Stap said he had used the handle “Umbreon” to extort victims and post their data on hacking forums. During that period he also worked as a software engineer at cybersecurity startup Hadrian and volunteered with the Dutch Institute for Vulnerability Disclosure. Security work and criminal activity coexisted in his admitted past. That history gives investigators an obvious reason to examine a possible connection when the same handle or imagery appears again. It cannot establish who carried out a later attack.
On September 9, van der Stap told KrebsOnSecurity he was trying to make amends. Sources subsequently told the publication he was arrested around the middle of the month. His account of his intentions and his 2023 conviction illuminate his history; the current investigation concerns alleged conduct that police have yet to describe publicly. Letting the old conviction fill that gap would assign a new attack before investigators have said what they suspect him of doing.
What an Umbreon Image Can Tell You
Umbreon is a Pokémon character as well as the name van der Stap said he used online. The character appeared in connection with a recent FBI breach and in a defacement of the Clop ransomware group's leak site amid activity attributed to ShinyHunters. Van der Stap's admitted use of the handle makes the overlap a lead someone might investigate. Whoever displayed the image in either incident did not thereby put a name on the work.
The character had also appeared in a 2020 HackForums defacement, BleepingComputer reported, before van der Stap created his Umbreon account in 2021. The HackForums defacement and the later incidents are separate events connected here by a displayed character, with no identified operator supplied by that match. The earlier appearance does not rule out his involvement in later activity. It shows how easily a recognizable symbol can travel between incidents. Anyone attributing an intrusion on that basis would need a connection to the person who controlled the relevant account or system.
Odido presents investigators with something different from a picture on a website. Police say its caller persuaded a help desk employee to enter credentials and a verification code into a fake login page, giving attackers access to internal systems. The employee faced a person claiming to be from IT, not an obviously malicious program. The attack turned a routine act of helping a colleague into a way past the login screen.
A recording preserves the caller's voice and the exchange. DataBreaches, which says it has spoken to van der Stap, told BleepingComputer that the recorded voice did not sound like him; a close friend reportedly reached the same conclusion. Those impressions offer a reason to be cautious about identifying van der Stap as the caller, though they are no substitute for a confirmed identification. Police have not publicly matched him to the call. Even establishing who spoke would answer only part of what happened at Odido: access through the fake page and the subsequent theft are related steps, potentially involving different people.
ShinyHunters has supplied its own competing statements. A person speaking for the group denied that van der Stap was associated with it when BleepingComputer asked. In remarks to Dutch news media recounted by KrebsOnSecurity, the group claimed the Odido caller was one of its members. The first claim concerns the reported suspect; the second concerns a caller whose identity has not been publicly established. Neither statement names the person who made the call. A group accused of extortion has an interest in how its membership is understood, so its claims cannot settle that identity question.
For Odido customers, the breach has already happened. The open question raised by this arrest is more precise: what conduct do police suspect this man of committing, and does it connect him to the February intrusion? Until they say, the conviction, the Umbreon image and the recorded call remain separate pieces of a case whose public account is still incomplete.
More Like This
ShinyHunters' FBI Claim Turns Credibility Into Leverage
ShinyHunters claims it breached the FBI via PeopleSoft. We separate verified facts from boasts and examine risks facing employees, applicants and spouses.
Claude Tag Wants to Run Your Workday
Anthropic's Claude Tag embeds AI directly into team Slack channels. Here's what it actually does, what it can't do yet, and what it means for how teams work.
Framer 3.0 Puts AI Agents on the Design Canvas
Framer 3.0 embeds AI agents directly on the design canvas. A hands-on demo shows what that actually means for web designers and startup founders.