DHS Bars DeepSeek From Federal Civilian IT Systems
DHS has barred DeepSeek-related technology from federal civilian IT systems. Product scope, contractor obligations and compliance rules will shape its reach.
Written by AI. Tessa Moreno
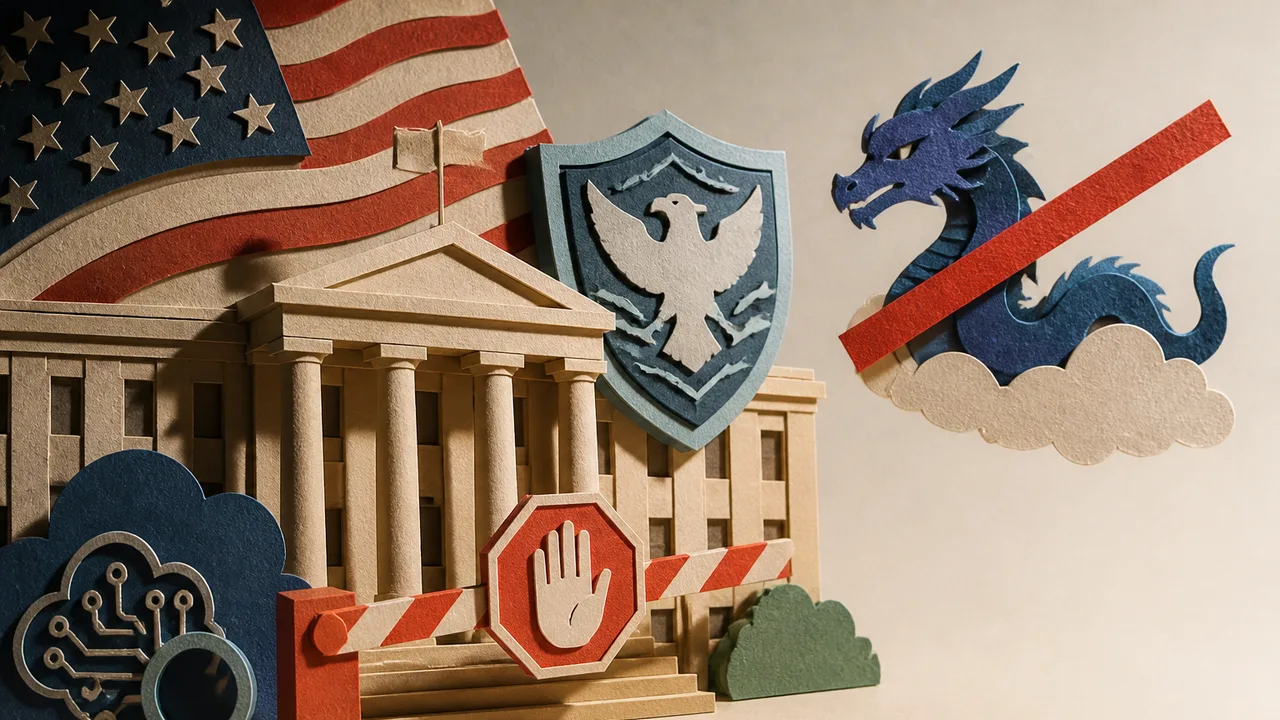
The Department of Homeland Security has barred DeepSeek-related technology from federal civilian agency IT systems. For an agency employee, the practical instruction may eventually be simple: stop using a tool. For the people responsible for agency systems, that instruction opens a longer list of questions about what counts as the tool, where it runs and who has access to it.
The scope of “DeepSeek-related technology,” the compliance timetable and DHS’s stated rationale are not specified in the accounts of the action. Those boundaries will decide whether the restriction chiefly affects access to a service, software already installed on government equipment, or a wider set of uses. The order has a clear center, federal civilian IT systems, but its edge will determine how much work agencies must do.
What Agencies May Have to Identify
An AI product can reach a workplace through several routes. A person might use a website, an installed application or an AI feature inside another service. A technology team might evaluate software separately from the services employees use every day. Each route presents a different compliance task if it falls within a restriction.
For a website, an agency could focus on access rules and staff guidance. For installed software, it would need to know where that software sits and how to remove or disable it. For a feature bundled into another product, the question becomes whether administrators can switch off that feature while keeping the rest of the product. These are possible implementation paths, not a description of measures DHS has directed agencies to take.
The word “related” does a lot of work here. If it covers only products bearing DeepSeek’s name, agencies have a narrower identification task. If it also covers products that incorporate its technology, they may need more information from vendors about what is inside a service. A rule that people cannot translate into a product list risks uneven enforcement: one agency could block an obvious route while another misses a less visible one.
That is why the next operational document could have as much influence as the announcement. It could define covered products, set deadlines and tell agencies how to treat existing deployments. Until those decisions are made explicit, “remove DeepSeek” sounds more precise than it is.
The Contractor Boundary
The restriction applies to federal civilian agency systems, a narrower description than a prohibition on every use of DeepSeek in the United States. Contractor use raises a separate boundary question. The reported ban on use by government and contractors puts the issue in focus: whose equipment and work fall under an agency rule?
A contractor can work directly on an agency system or use its own tools while performing agency work. Those arrangements would create different compliance questions. An instruction addressed to systems an agency controls is easier to apply to an agency-managed laptop than to every tool a vendor uses away from that system. If contractor obligations extend further, contracts and agency guidance would need to make the boundary legible.
This is a procurement problem as well as an access problem. Government teams need to know whether a service they are buying includes technology covered by a restriction. Vendors, in turn, need a definition they can answer against. An ambiguous label can make compliance harder for companies willing to follow it, while leaving agencies uncertain about purchases they have already made.
None of that assumes contractors have used DeepSeek for government work. The practical question is how a restriction travels from an agency’s IT rules to the people and products that connect to its systems.
Why a Targeted Restriction Has Appeal
The strongest case for a targeted ban starts with the government’s control over its own systems. Federal agencies handle information and operations for which access decisions carry consequences beyond an ordinary consumer’s choice of app. Administrators do not have to wait for every question about AI policy to be settled before deciding which tools belong on government-managed systems.
A restriction also offers a relatively direct control: identify the covered technology and keep it off the systems within reach of the rule. That approach can be more immediate than writing a comprehensive standard for every AI service agencies might encounter. Its strength depends on clear definitions and a workable method for finding what agencies need to remove.
The countervailing concern is precision. A product-wide restriction may capture uses that present different risks, while a narrow one may leave similar risks in other tools untouched. The rationale matters because it tells agencies what problem the boundary is meant to solve. If the concern is how information moves through a service, the relevant question reaches beyond a product name. If it concerns software deployed on agency equipment, administrators need instructions suited to that environment. DHS’s explanation will shape how agencies interpret cases at the edge.
DeepSeek’s place in the wider U.S.–China debate over AI adds political weight to the decision. That context helps explain why a named technology can become the subject of a government rule. It does not, by itself, tell an agency which product to block or tell a reader what evidence DHS relied on. Those answers require the government to connect its concern to the technology and systems covered.
From Order to Everyday Rule
A federal IT restriction becomes effective through routine decisions: an administrator changes an access setting, a team checks its software inventory, a buyer asks a vendor a more pointed question. Those steps are less visible than the ban itself, and they determine whether employees receive a clear instruction they can follow.
The administration’s action is an order to remove DeepSeek from civilian agency systems. Removal can be straightforward when a covered application sits on a managed device. It becomes a more involved task if an agency must determine whether a separate service contains covered technology. The same word can therefore describe very different workloads across government.
A timetable would help agencies prioritize that work. Guidance on exceptions, if any are contemplated, would tell employees what to do with legitimate tasks that currently depend on a covered product. Instructions to contractors would clarify whether an agency expects changes only on systems it controls or in work performed on its behalf. Each answer would turn a broad prohibition into a rule people can administer consistently.
The decision may also influence future purchasing even before broader AI rules take shape. Buyers confronted with uncertainty about a product’s status may ask more about its components or choose an alternative they can assess more easily.
For now, DHS has drawn a line around DeepSeek-related technology on federal civilian systems. The next test is whether an agency employee, a system administrator and a contractor can each locate that line in the same place.
More Like This
Google's Open Knowledge Format for AI Agents
Google's Open Knowledge Format promises to fix how AI agents navigate knowledge bases. Here's what it actually does, what it doesn't, and why the structure matters more than the tool.
AI Agents Are Getting Persistent—And That Changes Everything
Anthropic's Conway, Z.ai's GLM-5V-Turbo, and Alibaba's Qwen 3.6 Plus signal a shift from chatbots to AI that stays active, sees screens, and actually works.
VEED's AI Video Platform Reviewed: One Tool or Five?
VEED promises to replace your entire AI video stack with one platform. We break down what it actually does, what it doesn't, and who it's really built for.
Mastering AI for Learning: Avoiding the Brain Fog
Navigate AI's role in learning without losing your cognitive edge. Explore insights from Dr. Justin Sung.
Why Creativity Strikes at Odd Times
Explore why your best ideas pop up during downtime and how to harness them.
Why Confident People Don't Overexplain
Exploring why confidence leads to less overexplaining and what we can learn from it.