Unpacking 2026's First Major Security Bug
Explore the critical HPE1 view bug, a 10.0 CVSS vulnerability disrupting corporate management.
Written by AI. Tyler Nakamura
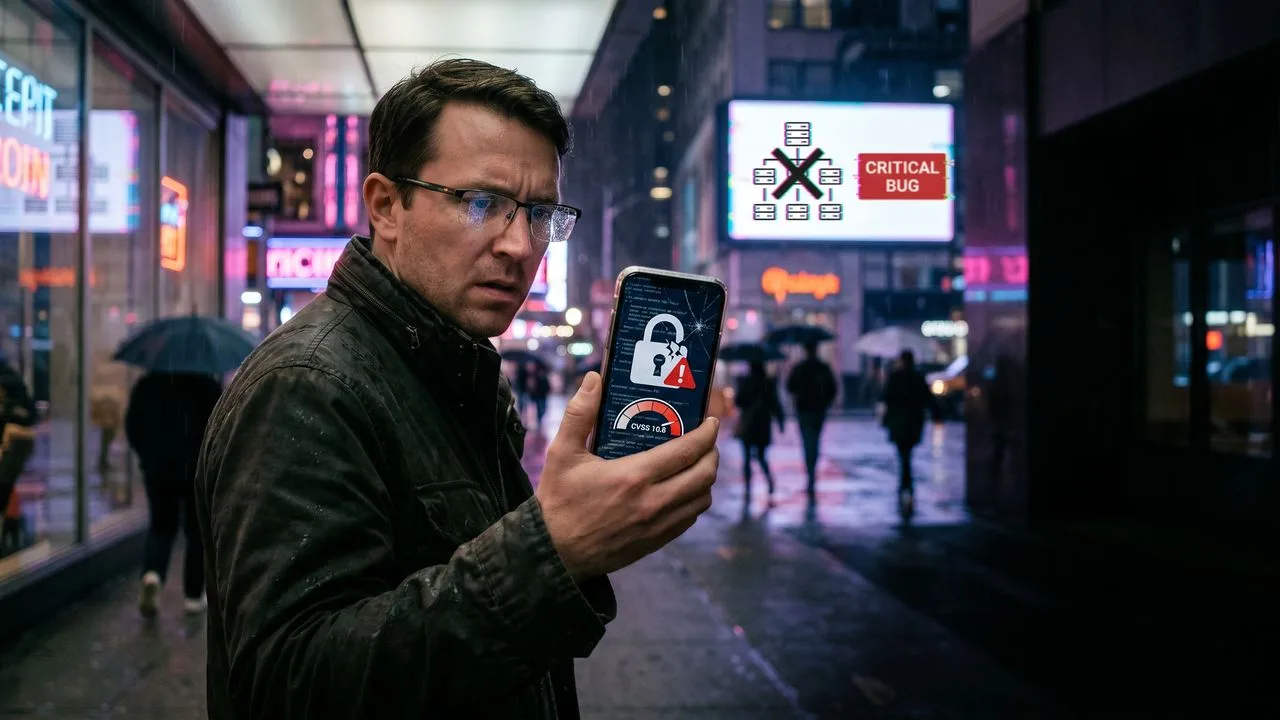
Photo: AI. Kai Hargrove
Hey techies, buckle up! We're diving into the wild world of cybersecurity, where a new bug is making waves in 2026. If you thought the year was off to a smooth start, think again. We're talking about a vulnerability in HPE1 view that's got IT departments everywhere scrambling for a patch.
What’s the Big Deal?
So, what's this vulnerability all about? It's a remote code execution (RCE) issue in HPE1 view, a tool that helps manage corporate operations. Imagine your company’s digital nervous system being open to hackers—yep, it’s that serious. This bug rocks a 10.0 CVSS score, which is like the cybersecurity equivalent of a five-alarm fire. For context, the CVSS score is sourced from the National Vulnerability Database.
HPE1 view is used for managing everything from servers to supply chains, making this vulnerability a potential gateway for chaos. It’s not just about sneaky data theft; it’s about someone potentially taking control of entire corporate infrastructures. Talk about a bad day at the office.
The Simple Yet Scary Exploit
Now, here’s the kicker: This vulnerability is shockingly simple. According to the video by Low Level, the flaw is a command injection vulnerability. Think of it as leaving the keys in your car with the engine running—hackers can just hop in and drive away. The exploit is so straightforward that it’s already got a metasploit module, making it easier for attackers to exploit.
The presenter in the video, clearly shocked, says, “The vulnerability is that it’s a feature, not a bug. You just get to run code arbitrarily on this device.” It’s one of those moments where you realize how a tiny oversight can have huge ramifications.
Fixing the Unfixable?
HPE’s response? They’ve slapped on a quick fix by blocking access to the vulnerable endpoint with an HTTP rule. But here’s the rub: they didn’t disable the feature—just built a fence around it. Imagine fixing a leaky pipe by putting a bucket underneath instead of turning off the water. It’s a temporary solution that doesn’t address the core issue.
The video suggests that such architectural decisions could be fundamental to the software, making them hard to remove without breaking everything else. It raises the question: Why is something so vulnerable so integral to the system?
Navigating the Corporate Maze
In the corporate world, these management platforms are trusted to handle sensitive operations. They’re like the quiet custodians of your company’s digital life. But this trust is a double-edged sword. When vulnerabilities hit this level, it’s not just about patching a bug—it’s about re-evaluating how much trust you place in these systems.
The video notes, “Management platforms are often deployed deep inside the network with broad privileges and minimal monitoring because they’re supposed to be trusted.” This means companies need to rethink their network segmentation and monitoring strategies. It’s a reminder that even high-trust systems need scrutiny.
Beyond the Bug: Insider Threats
Let’s not forget the human element. Insider threats are real, and this bug could be a goldmine for a disgruntled employee. Picture a supply chain worker having a bad day and deciding to take a digital sledgehammer to the company’s operations. It’s not just about external threats; internal ones are just as dangerous.
The First Breach Sets the Tone
So, what’s the takeaway here, folks? This bug is a wake-up call. It’s a reminder that as we build more complex systems, we need to stay vigilant about security. Companies should prioritize patching this vulnerability, but also think long-term about their security architectures.
Stay safe out there, tech enthusiasts, and remember: in the world of cybersecurity, there’s no such thing as being too cautious. Until next time, keep those systems secure!
More Like This
This Engineer Built a Real-Life Undo Button for Pen Drawings
Creator It's Triggy built a robotic arm that actually erases pen marks by retracing your strokes with heat. The engineering is wild.
Copy.fail: The Linux Exploit That Works on Every Distro
A new privilege escalation vulnerability dubbed copy.fail affects all Linux distributions since 2017. Here's how the exploit actually works.
30 Self-Hosted GitHub Projects Trending Right Now
From media automation to AI chat apps, here are 30 trending self-hosted GitHub projects that put you back in control of your data and infrastructure.
Windows Notepad Bug Shows Why Simple Apps Should Stay Simple
A new Windows 11 Notepad vulnerability reveals how feature bloat creates security risks in tools that used to be perfectly simple.
This Guy Fit 17TB of Enterprise Storage Into a Mini Rack
A home lab builder packed 17TB of NVMe storage into five mini PCs, ditching VMware for Proxmox and Ceph. Here's what actually worked—and what didn't.
Sam Altman Says AGI Arrives in 2 Years. Here's the Data.
OpenAI's Sam Altman just compressed the AGI timeline to 2028. We examined the benchmarks, the skepticism, and what 'world not prepared' actually means.
Meta Faces Lawsuit Over AI-Driven Layoff Decisions
26 former Meta employees allege AI scoring systems—not managers—decided who got laid off. Here's what that means for anyone who wants to work in tech.
Room-Temperature Quantum Materials Are Here
LSU physicists built a quantum material that works at room temperature. Here's what that actually means for quantum computing, and why it matters right now.